SASE for Remote and Hybrid Work: Secure Access for Distributed Teams
Assess how SASE can support remote users, branches, SaaS, and private applications by connecting identity, application paths, and security controls without assuming every workforce needs a new platform.
By Mark Poulton
SASE for Remote and Hybrid Work: Secure Access for Distributed Teams
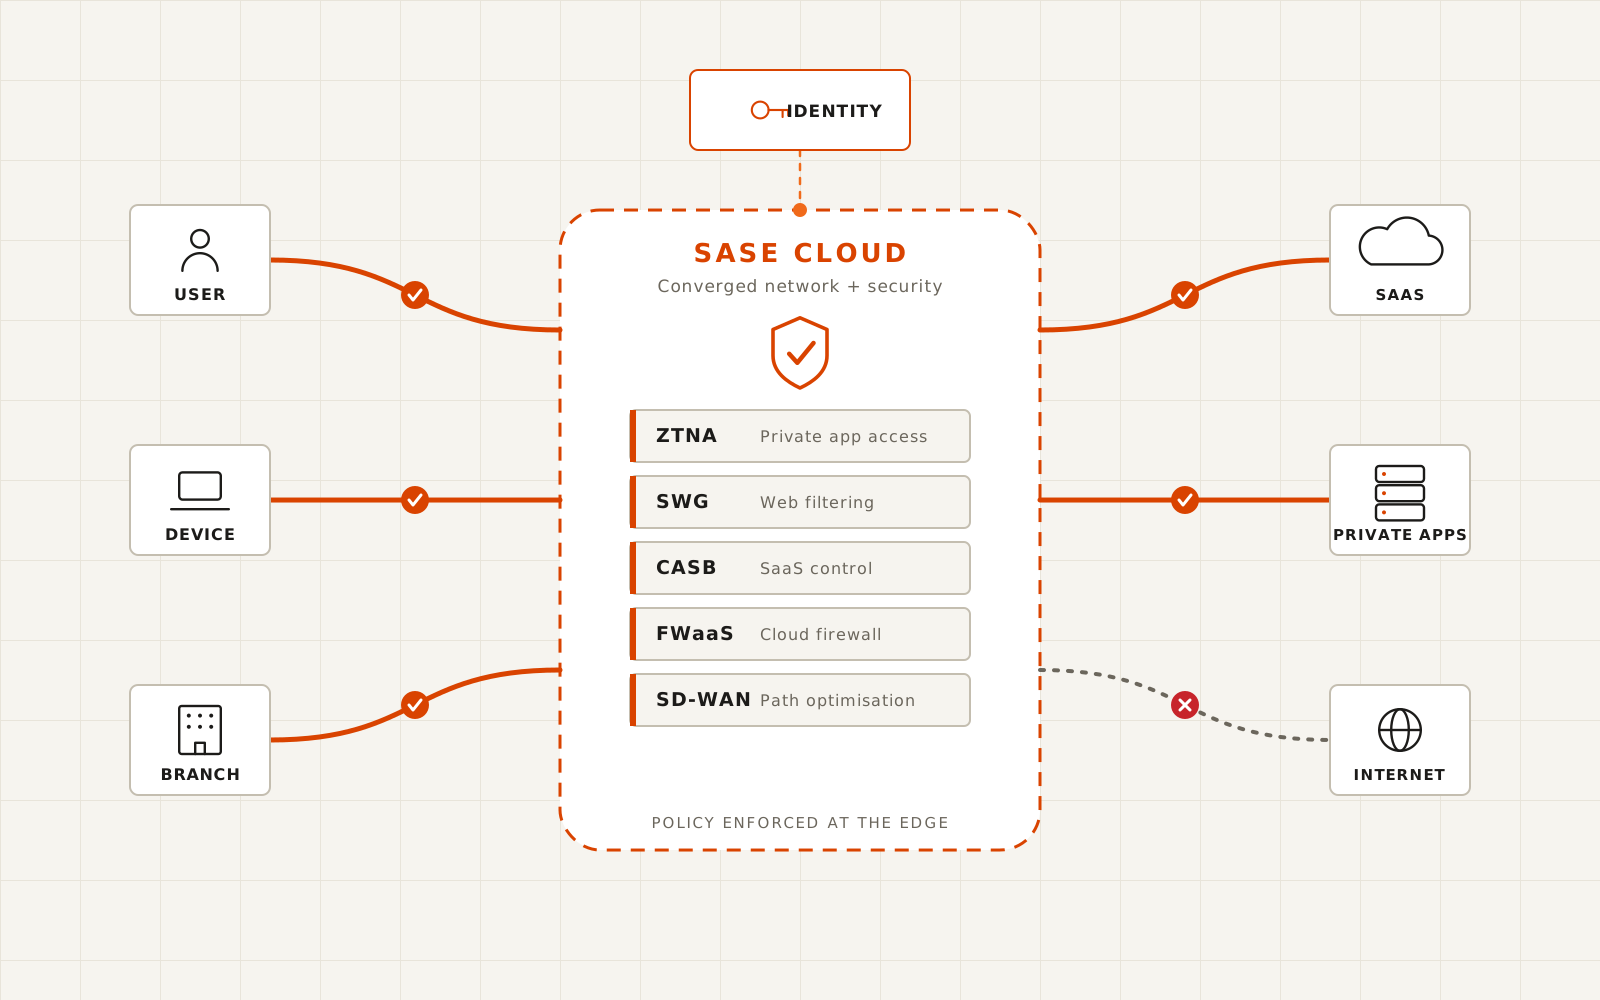
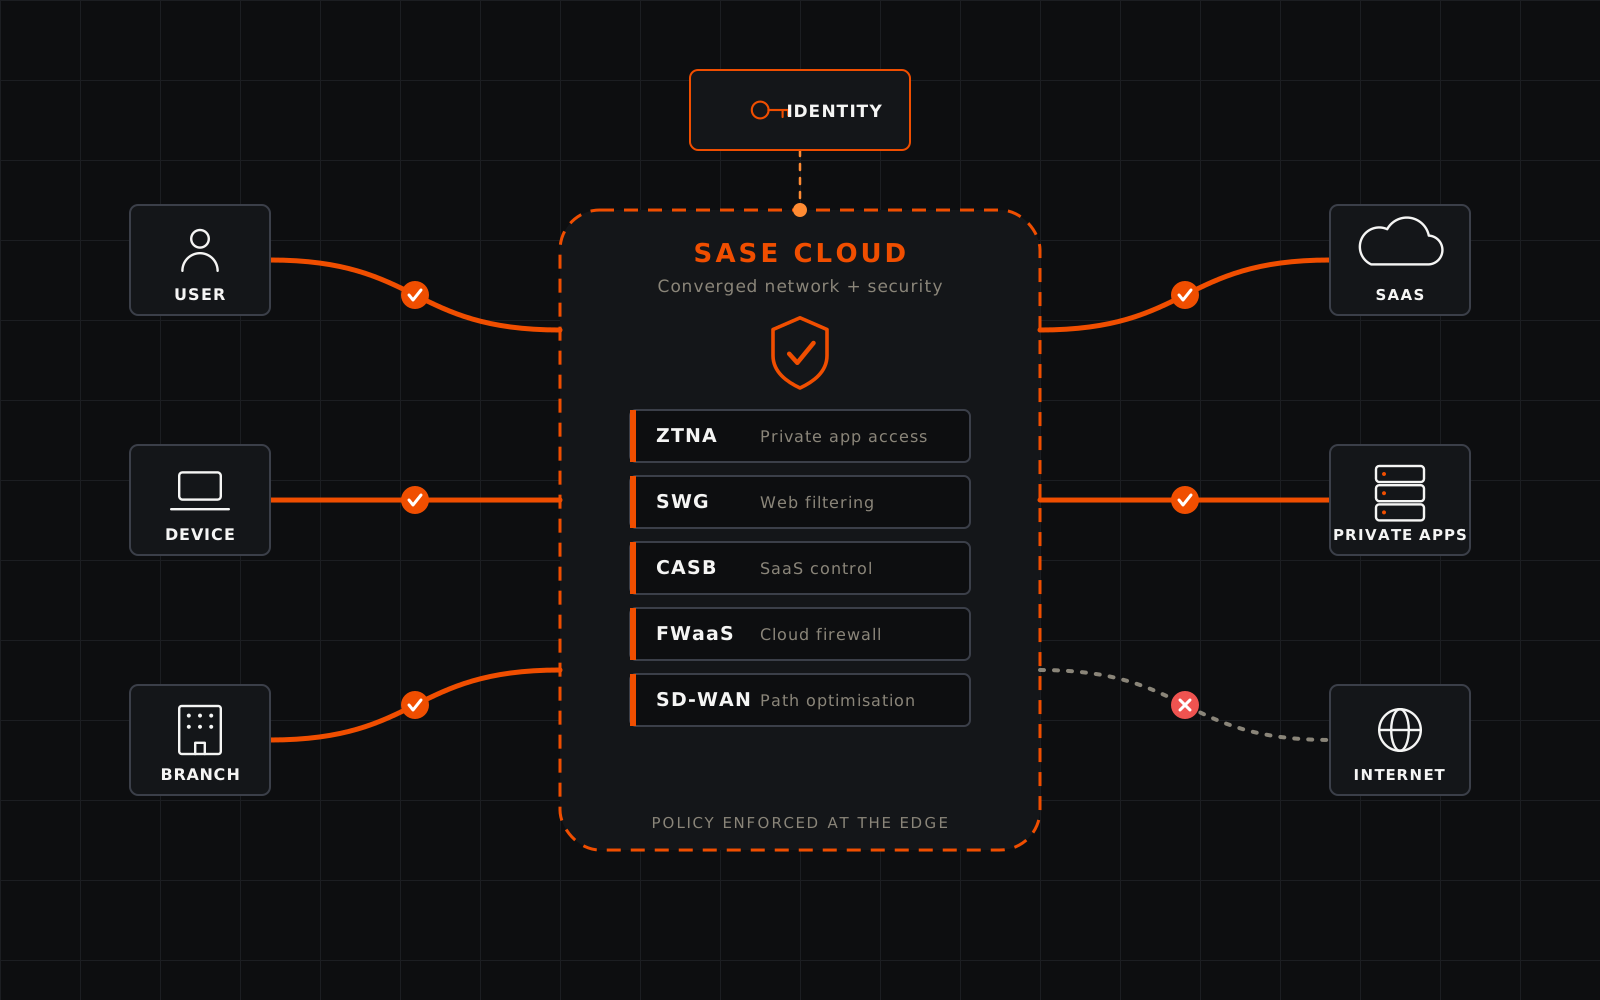
SASE can support remote and hybrid work by coordinating network paths with security controls for users accessing SaaS, private applications, and services hosted across different locations. Its practical value depends on the access problem: which person or device needs which resource, how identity and device context are checked, where traffic travels, and who monitors and supports the path. Remote work alone does not make SASE necessary.
SASE brings networking and security capabilities together; it is not a synonym for a remote-access client. The SASE fundamentals article defines the model and its relationship to SD-WAN and SSE. This article focuses on distributed-access situations.
Which remote-work access paths might SASE support?
The useful unit of analysis is a user-to-application path, not a generic “remote worker.” A single person may use SaaS, a private business application, and a branch-hosted service, each with different security and routing needs.
| Access situation | What the design needs to decide | Evidence to check |
|---|---|---|
| Remote user to SaaS | Whether traffic can go directly to the service or should pass through a security point; which web and cloud-app policies apply. | Application response from representative locations, policy coverage, logging, and user impact when a control blocks access. |
| Remote user to a private application | Which user and device may reach the application, what identity and context are required, and whether access can be limited to that resource. | Authentication and device signals, least-privilege scope, application compatibility, and the exception process. |
| Branch or campus user to cloud services | How the site selects an internet or WAN path and where security inspection occurs. | The end-to-end route, inspection point, failover behaviour, support boundary, and application experience. |
| Partner or contractor to a defined workflow | How external identities are governed and how access ends when the engagement changes. | Identity lifecycle, time-bounded access, audit events, and named owners for approval and removal. |
These are evaluation scenarios, not a checklist that every SASE service implements identically. Capabilities such as secure web gateway, cloud access security broker, zero-trust network access, and firewall as a service may be combined differently. Confirm the actual traffic and policy behaviour in the proposed service.
How do identity, applications, and security controls fit together?
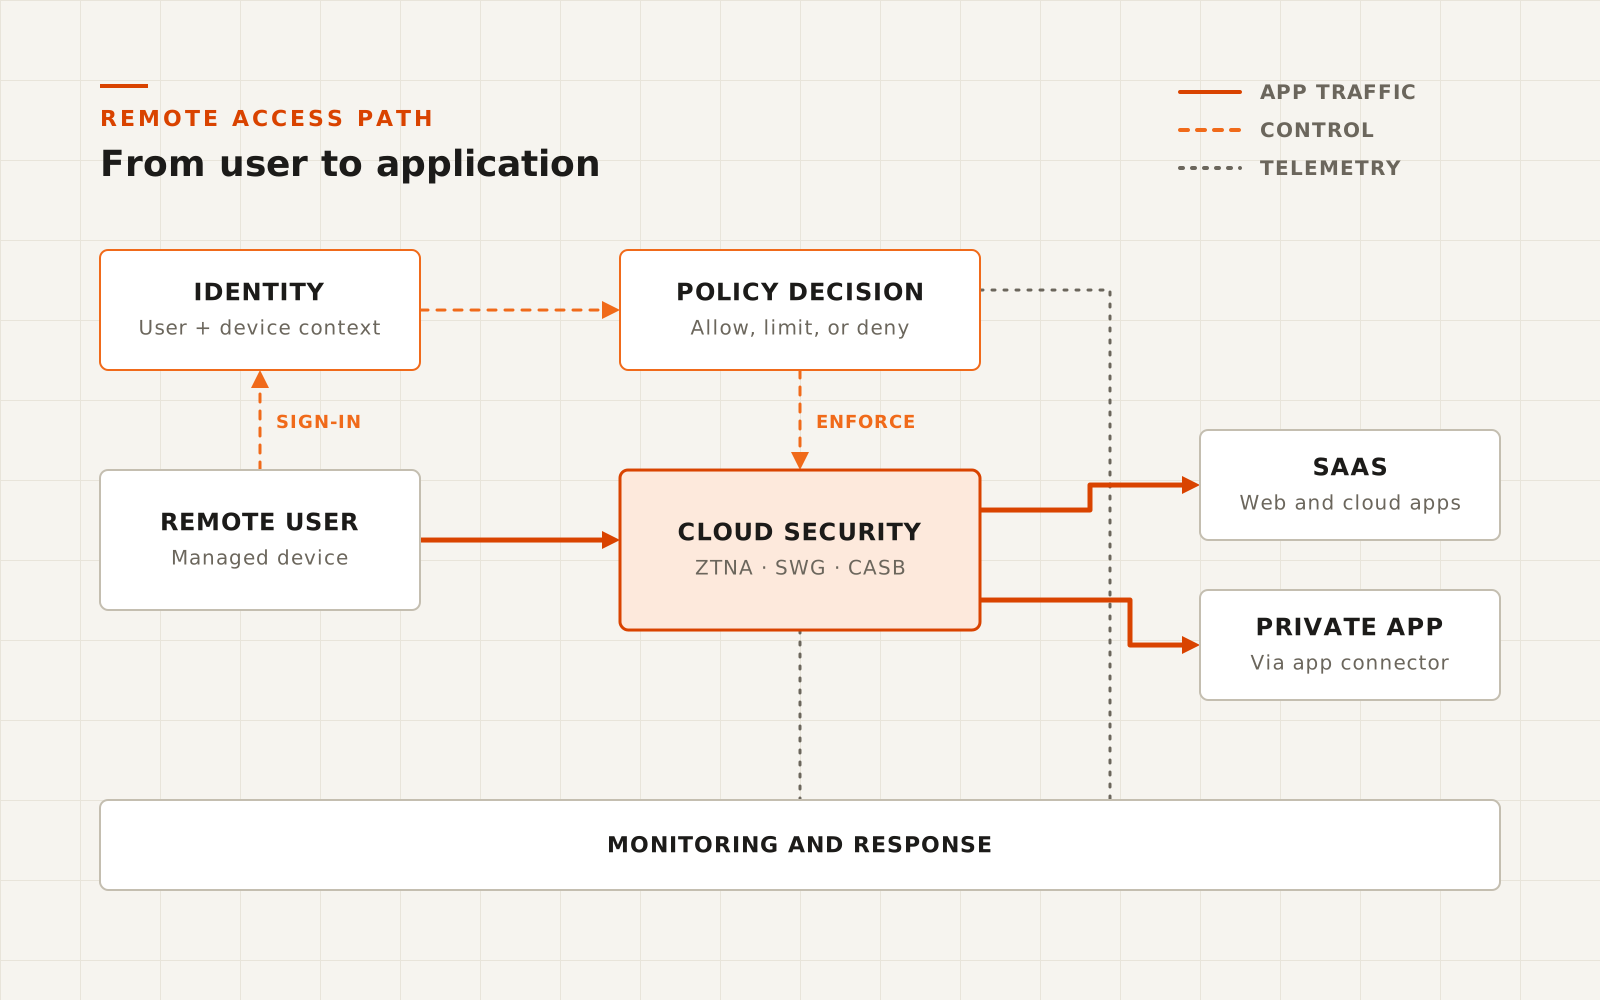
Access policy should connect a known identity and, where available, device context to a specific application or resource. ZTNA is one approach for limiting access to private applications; it does not replace identity governance, endpoint protection, application authorisation, or incident response. For web and SaaS paths, confirm which traffic is inspected, how exceptions are handled, and which events reach the teams responsible for investigation.
Map the complete route: user device, local network, access service, security enforcement, application, and return traffic. Note where encryption ends, what information a provider processes, how identity or device signals are shared, and what happens if a service point or connection is unavailable. A cloud service close to a user may reduce unnecessary backhaul in some designs, but actual performance depends on service location, routing, application hosting, and provider capacity. Measure it rather than assuming it.
The SD-WAN Deep Dive covers site connectivity and traffic steering. SASE may use SD-WAN for branch paths, but it does not require replacing a suitable SD-WAN deployment. The SD-WAN security article further separates network controls from broader identity and cloud-security responsibilities.
What trade-offs matter for distributed teams?
Application experience and service location
Check where users, applications, and the provider's enforcement points are located. Test common and latency-sensitive workflows from representative offices and home-network conditions. A security service can add a routing hop; direct access can change where policy is applied. Neither path is automatically faster or safer.
Identity and device readiness
Consistent access depends on usable identity sources, lifecycle processes, and reliable device signals. Define what happens when a device is unmanaged, a signal is unavailable, or a legitimate user is blocked. Emergency and support access need explicit owners and review.
Visibility and operational ownership
Agree which team reviews access events, investigates incidents, updates policy, and coordinates with the provider. Confirm that logs include enough context to investigate without assuming that centralised dashboards automatically create a unified operating model.
Coexistence and service dependency
Existing VPNs, firewalls, web controls, and SD-WAN may remain during a transition or continue to serve specific paths. Map overlapping enforcement, contract terms, failover, and escalation before changing a user's route. The SASE implementation article covers architecture and staged rollout in depth.
When might SASE be unnecessary?
If a small set of remote users already reaches a limited number of applications through a well-managed access service, improving that service may be more proportionate than adopting a wider SASE platform. Existing controls may also meet requirements for a distributed workforce when policy, visibility, and support are effective. Compare the current design against the actual gaps, including operating effort and cost, rather than treating a work-location change as an architecture mandate.
For wider organisational fit, continue to how SASE can support business transformation. The SD-WAN-to-SASE transition article addresses organisations explicitly evaluating that migration question.
Conclusion
SASE is worth considering when distributed access exposes a concrete gap in how network paths, identity, and security policy are coordinated. Evaluate real user-to-application flows, test experience and failure behaviour, and assign operational ownership before selecting a service. The right outcome may be SASE, a narrower capability, or a well-run existing design.